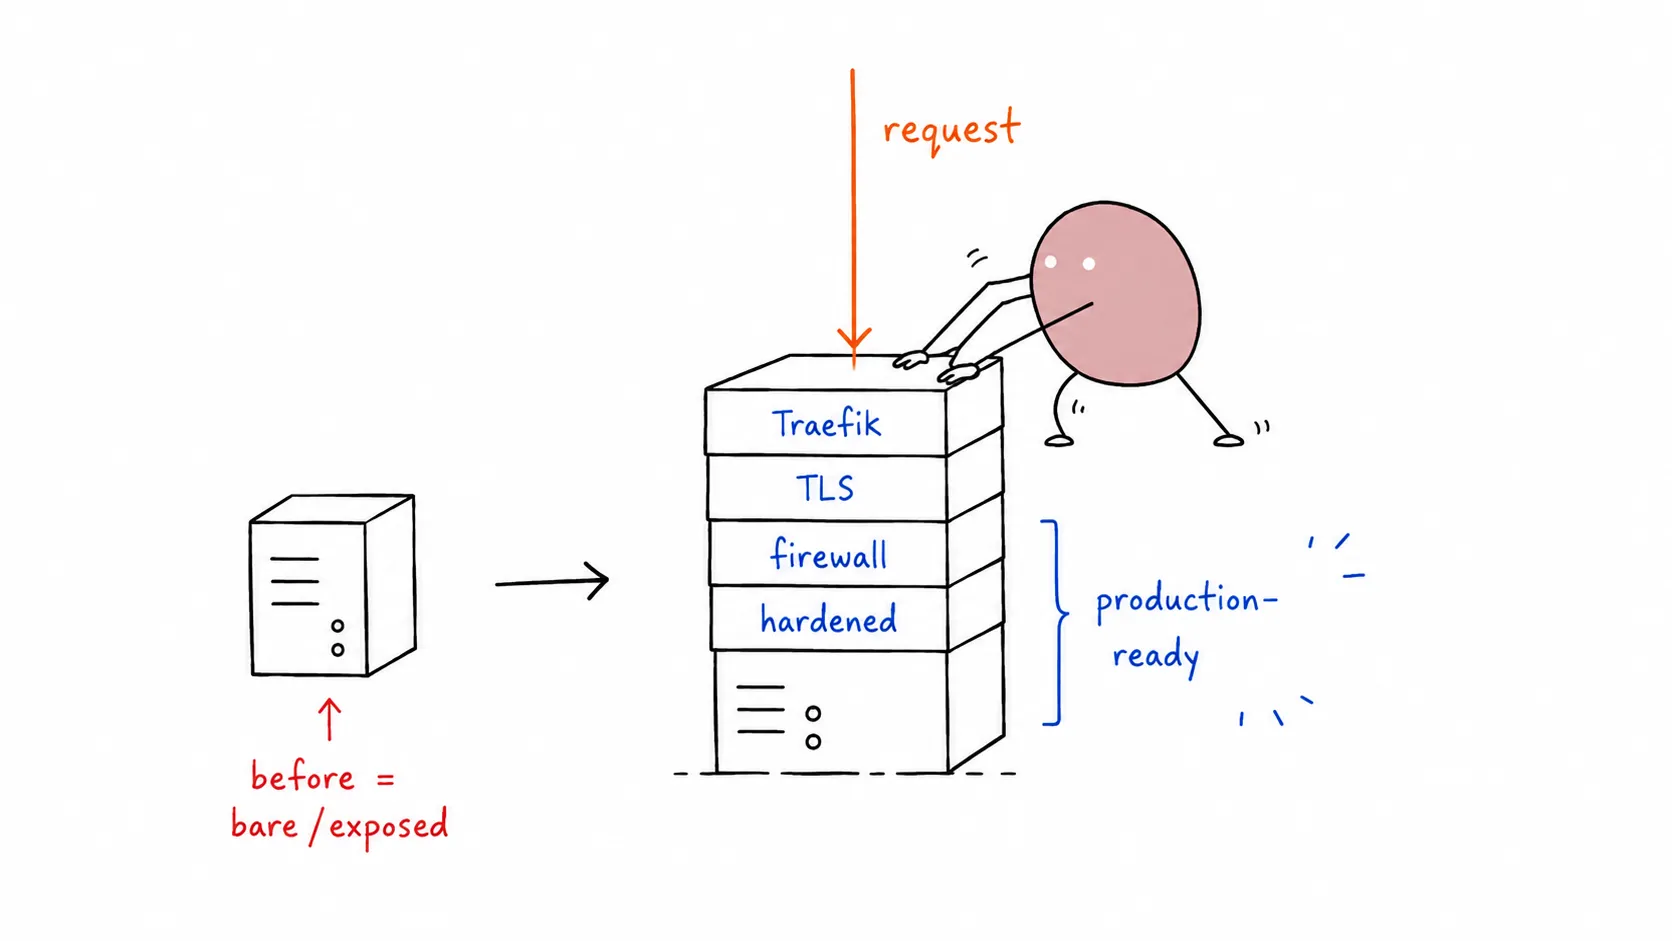
Setting Up a Production-Ready VPS from Scratch: Rocky Linux 10 & Ubuntu 26.04
Adapted from Dreams of Code, a dual-OS guide covering both RHEL-family and Debian-family setups.
Deploying to the cloud has never been easier. Platform-as-a-Service (PaaS) options like Railway, Fly.io, and Render make going live a breeze. But PaaS isn’t perfect for every use case: long-running tasks, heavy data transfer, and predictable billing often push teams toward a VPS (Virtual Private Server).
The perceived difficulty of hardening and configuring a raw VPS scares people off. But is it actually hard? We set out to prove it isn’t. Here’s a production-ready stack on both Rocky Linux 10 and Ubuntu 26.04 LTS.
What “Production-Ready” Means Here
DNS pointing to the server
Application deployed and running (Docker)
HTTPS/TLS with automatic cert provisioning & renewal (Let’s Encrypt)
Hardened SSH: no root login, no password auth
Firewall blocking unnecessary ports
High availability: multiple app instances
Load balancing via reverse proxy
Automated rolling deployments
Uptime monitoring with alerts
Constraints: No Kubernetes. No Coolify. No Terraform. Simple tooling, minimal domain expertise.
Step 1: Provisioning the VPS
Pick a provider (Hetzner, Hostinger, DigitalOcean, Vultr). We used a 2 vCPU / 8 GB RAM instance.
💡 Hosting with a side of nasi goreng? 🇮🇩 8labs offers VirtualLabs and ElasticLabs : VPS and scalable infrastructure, straight out of Indonesia. 🤙
During setup via your provider’s panel:
Select Rocky Linux 10 or Ubuntu 26.04 LTS
Set a strong root password
Add your SSH public key
Disable any “malware scanner” or monitoring agent if you don’t need it
Once deployed, test SSH:
ssh root@<your-server-ip>
Step 2: Create a Non-Root User
Working as root is a bad habit. Create a regular user with sudo/wheel privileges.
Clear any existing A/AAAA/CNAME records at your registrar
Add an A record for @ (root domain) pointing to your server’s IPv4
Optionally add a www CNAME pointing to @
Find your server IP:
ip -4 addr show | grep inet# orcurl -4 ifconfig.me
DNS propagation takes minutes to hours. Move on to security while waiting.
Step 4: Harden SSH
SSH is your front door. Lock it down.
4a. Generate and copy your SSH key
If you don’t already have an SSH key pair, generate one on your local machine:
ssh-keygen -t ed25519 -C "your-email@example.com"# Press Enter to accept the default path (~/.ssh/id_ed25519)# Set a passphrase (recommended) or leave empty
Ed25519 vs RSA: Ed25519 is faster, more compact, and just as secure as RSA 4096. It is supported by OpenSSH 6.5+ (released 2014), so it works on every modern server. Only use RSA 4096 if you need to connect to legacy servers running pre-2014 OpenSSH:
If you already have an SSH key, skip the generation step and jump straight to ssh-copy-id.
Test key-based login before proceeding:
ssh deployer@<server-ip>
4b. Simplify with SSH config (optional)
Typing ssh deployer@203.0.113.42 every time gets old. Add an entry to your local ~/.ssh/config:
Host prod-server HostName 203.0.113.42 User deployer IdentityFile ~/.ssh/id_ed25519Host myapp.com HostName myapp.com User deployer IdentityFile ~/.ssh/id_ed25519
Now you can connect with just:
ssh prod-serverssh myapp.com
Tip: Use short, memorable Host aliases. The HostName can be either an IP address or a domain name. If you’re managing multiple servers, add an entry for each one — your fingers will thank you.
4c. Edit sshd_config
sudo vim /etc/ssh/sshd_config
Set or uncomment these lines:
PasswordAuthentication noPermitRootLogin noPubkeyAuthentication yes# Rocky: also check /etc/ssh/sshd_config.d/*.conf for overrides# Ubuntu: also check /etc/ssh/sshd_config.d/50-cloud-init.conf
4d. Clean up cloud-init overrides
Cloud images often ship a drop-in that re-enables password auth. Check and fix:
sudo vim /etc/ssh/sshd_config.d/50-cloud-init.conf# Comment out or delete any PasswordAuthentication yes line
4e. Reload and Verify
sudo systemctl reload sshd# This MUST fail:ssh root@<server-ip># Permission denied (publickey) ← good# This MUST work:ssh deployer@<server-ip>
⚠️ Do not close your current SSH session until you’ve verified a new session works. Open a second terminal for testing.
Step 5: Firewall
Rocky uses firewalld by default (not ufw).
# Check statussudo systemctl status firewalld# If not running, install and start:sudo dnf install -y firewalldsudo systemctl enable --now firewalld# Default zonessudo firewall-cmd --get-default-zone # usually 'public'# Allow SSH (CRITICAL: do this first)sudo firewall-cmd --permanent --add-service=ssh# Reload to applysudo firewall-cmd --reload# Verifysudo firewall-cmd --list-all
# Enable UFWsudo ufw default deny incomingsudo ufw default allow outgoing# Allow SSH (CRITICAL: do this first)sudo ufw allow 22/tcp# Enablesudo ufw enable# Verifysudo ufw status verbose
Docker bypass warning: Docker manipulates iptables directly, which can bypass both firewalld and ufw rules for published ports. The solution: don’t publish container ports directly. Use a reverse proxy (Step 7) and only expose ports 80/443 on the host.
Step 6: Install Docker
# Remove old Docker packages if anysudo dnf remove -y docker docker-client docker-client-latest docker-common \ docker-latest docker-latest-logrotate docker-logrotate docker-engine# Add Docker reposudo dnf config-manager --add-repo https://download.docker.com/linux/rhel/docker-ce.repo# Install Dockersudo dnf install -y docker-ce docker-ce-cli containerd.io docker-buildx-plugin docker-compose-plugin# Start and enablesudo systemctl enable --now docker# Add user to docker groupsudo usermod -aG docker deployer# Verifydocker --versiondocker compose version
Traefik automatically obtains and renews Let’s Encrypt certificates. The acme.json file stores them. Keep it safe (600 permissions, handled by Docker volume).
Step 11: Automated Deployments with Watchtower
Watchtower monitors Docker image registries and updates running containers when new images appear.
Add to compose.yaml:
services:
  watchtower:
    image: containrrr/watchtower
    command:
      - "--label-enable"          # Only update containers with the label
      - "--interval"
      - "30"                      # Check every 30 seconds
      - "--rolling-restart"       # One container at a time (for multi-replica)
    volumes:
      - /var/run/docker.sock:/var/run/docker.sock:ro
Now when you push a new image to ghcr.io/yourusername/guestbook:prod, Watchtower picks it up within 30 seconds and performs a rolling restart, zero downtime.
Step 2: Apply the fix. Set the SELinux context for the blocked path(s):
# Replace /path/to/mount with the actual path from ausearch outputsudo semanage fcontext -a -t container_file_t "/path/to/mount(/.*)?"sudo restorecon -Rv /path/to/mount
For Docker named volumes, the path is typically under /var/lib/docker/volumes/<volume-name>/. For bind mounts, use the host path from your docker-compose.ymlvolumes: section.
Usually Docker and SELinux coexist fine on Rocky 10 with default policies. Only intervene if you see Permission denied in container logs despite correct file permissions.
Checklist
Non-root user created with sudo/wheel
SSH: PasswordAuthentication no, PermitRootLogin no
Firewall: only 22, 80, 443 open
Docker installed, user in docker group
App running as docker compose up -d
Traefik reverse proxy routing traffic
HTTPS active with Let’s Encrypt auto-renewal
Multiple app replicas running
Watchtower handling rolling updates
Uptime monitor configured with alerts
Setting up a production-ready VPS is less intimidating than it looks. Traefik + Watchtower + Docker Compose gives you 90% of what a PaaS offers : with more control, predictable billing, and no vendor lock-in. Both Rocky Linux 10 and Ubuntu 26.04 make excellent foundations; pick the ecosystem you’re most comfortable with.